Data

Conferences

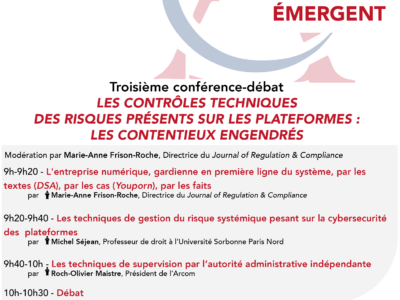
🎤Le Contentieux Systémique Emergent du fait du système numérique (“emerging systemic litigation arising from the digital system”), in 🧮Importance et spécificité du Contentieux Systémique Émergent, cycle de conférences-débats “Contentieux Systémique Émergent”

► Full Reference: M.-A. Frison-Roche, "Le Contentieux Systémique Emergent du fait du système numérique ("emerging systemic litigation arising from the digital system"), in Les contrôles techniques des risques présents sur les plateformes et les contentieux engendrés (Technical controls on the risks present on platforms and the disputes that arise), in cycle of conferences-debates "Contentieux Systémique Émergent" ("Emerging Systemic Litigation"), organised on the initiative of the Cour d'appel de Paris (Paris Cour of Appeal), with the Cour de cassation (French Court of cassation), the Cour d'appel de Versailles (Versailles Court of Appeal), the École nationale de la magistrature – ENM (French National School for the Judiciary) and the École de formation des barreaux du ressort de la Cour d'appel de Paris – EFB (Paris Bar School), under the scientific direction of Marie-Anne Frison-Roche, May 27,2024, 9h-10h30, Cour d'appel de Paris, Cassin room - 🧮see the full programme of this event - 🧮see the full programme of the entire cycle Contentieux Systémique Émergent (Emerging Systemic Litigation) - 🔲see the slides (in French), basis of this conference - 🌐read on  LinkedIn the summary of this conference les slides - 🎤read  the presentation of the second conference in this manifestation: "Un contentieux systémique in vivo : le cas dit des sites pornographiques" ("a Systemic Litigation in vivo: the case of pornographic prestations platforms") - 🧱read the general presentation of this scientific coordination of this manifestation and its various speechs - 🌐read on LinkedIn the summary of this manifestation in the Newsletter MAFR Regulation, Compliance, Law - ► Summary of this conference: This speech is a prelude to the three more specific speeches and aims to show how the digital system, by its very nature, produces and will produce "Systemic Litigation".  Systemic Litigation" is defined by "cases" (a procedural notion) brought before judges, who may be judges of first instance, or possibly emergency judges, in which the interests, or even the future, of a system are involved beyond the dispute between the parties.  This Systemic Case may be brought before a specialised judge, including the juridictional body of a Regulatory or Supervisory Authority, but also before a judge of ordinary Law, on the basis of a special text but possibly on the basis of a text of ordinary Law. This can lead to a fragmentation of litigation, even though the unity of the system remains, or even is at stake, in the present and in the future. The "digital system" is an example of the "natural" production of Systemic Litigation which arise as a result of the Digital System alone, in particular because of the systemic risks inherent in this system, and the fact that their prevention and management are internalised in the operators who have built and manage the system (Compliance Law). The issue is therefore one of Interregulation. Platforms in particular give rise to Systemic Litigation because of the specific nature of certain risks, for example disinformation, terrorism, destruction of rights (copyright being just one example), the risk of minors having access to content that is destructive for them, and so on. Digital Systemic Litigation has only just begun. It is essential that judges are prepared for this and that they face up to it together through dialogue.             - 🌐follow Marie-Anne Frison-Roche on LinkedIn 🌐follow Marie-Anne Frison-Roche on Instagram 🌐subscribe to the Newsletter MAFR Regulation, Compliance, Law

Articles

💬”Let’s Use the Power of GAFAMs in the Service of General Interest!” (“Utilisons la puissance des GAFAMs au service de l’intérêt général!”)

Full reference: Frison-Roche, M.-A., "Let's Use the Power of GAFAMs in the Service of General Interest!" ("Utilisons la puissance des GAFAMs au service de l'intérêt général!"), interview done by Olivia Dufour, Actu-juridiques Lextenso, 11st of January 2021 Read the interview (in French) To read the article translated in English by us, read the working paper on which this interview is based   Summary of the interview by Olivia Dufour: Marie-Anne Frison-Roche, Professor of Regulation and Compliance Law, reported to the government in 2019 about Internet governance. For this expert, giving a disciplinary power to GAFAMs is the only effective solution. And the suppression of Donald Trump's account is not likely to call this analysis into question.   The three questions (translated in English here by ourselves) asked by Olivia Dufour are:  The deletion of Donald Trump's Twitter account arouses strong emotions on social networks, and not only among his supporters. What do you think about this ? However, this incident does raise concern. Are we not giving too much power to these private companies? This raises the question in France of the relevance of the Avia system … Should we therefore resolve by default to give our freedoms to private and opaque mastodons?   Read the answers to these three questions (in French)   To go further, especially about the logics that guide the Avia system, see: Frison-Roche, M.-A., "Hate on internet: we need to responsibilize digital operators" ("Haine sur internet: il faut responsabiliser les opérateurs numériques"), 2020 Frison-Roche, M.-A., The contribution of Compliance Law to Internet Governance, report to Government, 2019

Books

VERGNOLLE, Suzanne

L’effectivité de la protection des personnes par le droit des données à caractère personnel (The effectiveness of the protection of people by personal data Law)

Full reference: Vergnolle, S., L'effectivité de la protection des personnes par le droit des données à caractère personnel (The effectiveness of the protection of people by personal data Law (our translation)), Passa, J. (dir.), thesis, Law, Panthéon-Assas University (Paris II), 2020, 531 p.   Read the thesis (in French) Read directly and only the table of contents (in French)     To go further about regulation of personal data, read:  Frison-Roche, M.-A., Rethinking the world from the notion of data, 2016 Frison-Roche, M.-A., The regulatory conséquences of a world redesigned from the concept of data, 2016. 

Articles

💬Facebook: Quand le Droit de la Compliance démontre sa capacité à protéger les personnes (Facebook: When Compliance Law proves its ability to protect people)

Full reference: Frison-Roche, M.-A., Facebook: Quand le Droit de la Compliance démontre sa capacité à protéger les personnes (Facebook: When Compliance Law proves its ability to protect people), interview with Olivia Dufour, Actu-juridiques Lextenso, 23rd of November 2020 Read the interview (in French) Read the news of the Newsletter MAFR – Law, Compliance, Regulation about this question

Videos

🎥Compliance Law, an adequate legal framework for GAIA-X, in 🧮GaiaX Summit2020, The World with GAIA-X

► Full Reference: M.-A. Frison-Roche, "Compliance Law, an adequate legal framework for GAIA-X", in Pan-European GAIA – X Summit, The World with GAIA-X, November18, 2020. - 🧮See the general presentation of the Summit - 📈​See the slides, basis of this intervention. - ► Summary of the intervention: Europe may offer an adequate legal framework for the GAIA-X project through Compliance Law. Compliance Law is a new form for Regulatory Law, driven by "Monumental Goals", negative Monumental Goals, for instance prevention of systemic failures, and positive Monumental Goals, for instance innovation or stability. This very new branch of Law works on these Monumental Goals, which must be explicit and internalized in Crucial Enterprises. These Crucial Enterprises concretize these Goals, supervised by public Authorities.  European Compliance Law already works, for instance about Personal Data protection (case law and GDPR) or prevention banking systemic failures (Banking Union), Compliance Tools being in balance with Competition principle. European Union Law is moving from the Ex-Post Competition Law to the Ex-Ante Compliance Law, internalizing Monumental Goals in Crucial Enterprises.  There is a perfect adequacy between European Compliance Law and GAIA-X. This project built by Crucial Enterprises must be supervised by public authority, maybe a specific or the European Commission. The governance of GAIA-X must be transparent and accountable. This private organization must use it powers in respect of the proportionality principle, controlled by the public supervisory body. The legal framework is required but it is sufficient.  - 📈see the slides, basis of this intervention. - 🎥watch the video of this intervention.  -    

Articles

Due process and Personal Data Compliance Law: same rules, one Goal (GCEU, October 29, 2020 Order, Facebook Ireland Ltd v/ E.C.)

Full reference: Frison-Roche, M.-A., Due process and Personal Data Compliance Law: same rules, one Goal (CJEU, Order, October 29, 2020, Facebook Ireland Ltd v/ E.C.), Newsletter MAFR – Law, Compliance, Regulation, 1st of November 2020 Read by freely subscribing other news of the Newsletter MAFR – Law, Compliance, Regulation Read Marie-Anne Frison-Roche's interview in Actu-juridiques about this decision (in French)   Summary of the news:  As part of a procedure initiated for anti-competitive behaviors, the European Commission has three times requested, between the 13th of March and the 11th of November 2019, from Facebook the communication of information, reitarated in a decision in May 2020.   Facebook contests it alleging that the requested documents would contain sensitive personal information that a transmission to the Commission would make accessible to a too broad number of observers, while "the documents requested under the contested decision were identified on the basis of wideranging search terms, (…) there is strong likelihood that many of those documents will not be necessary for the purposes of the Commission’s investigation".  The contestation therefore evokes the violation of the principles of necessity and proportionality but also of due process because these probatory elements are collected without any protection and used afterwards. Moreover, Facebook invokes what would be the violation of a right to the respect of personal data of its employees whose the emails are transferred.  The court reminds that the office of the judge is here constraint by the condition of emergency to adopt a temporary measure, acceptable by the way only if there is an imminent and irreversible damage. It underlines that public authorities benefit of a presumption of legality when they act and can obtain and use personal data since this is necessary to their function of public interest. Many allegations of Facebook are rejected as being hypothetical.  But the Court analyzes the integrality of the evoked principles with regards with the very concrete case. But, crossing these principles and rights in question, the Court estimates that the European Commission did not respect the principle of necessity and proportionality concerning employees' very sensitive data, these demands broadening the circle of information without necessity and in a disproportionate way, since the information is very sensitive (like employees' health, political opinions of third parties, etc.).  It is therefore appropriate to distinguish among the mass of required documents, for which the same guarantee must be given in a technique of communication than in a technic of inspection, those which are transferable without additional precaution and those which must be subject to an "alternative procedure" because of their nature of very sensitive personal data.  This "alternative procedure" will take the shape of an examination of documents considered by Facebook as very sensitive and that it will communicate on a separate electronic support, by European Commission's agents, that we cannot a priori suspect to hijack law. This examination will take place in a "virtual data room" with Facebook's attorneys. In case of disagreement between Facebook and the investigators, the dispute could be solved by the director of information, communication and medias of the Directorate-General for Competition of the European Commission.  - We can draw three lessons from this ordinance:  This decision shows that Procedural Law and Compliance Law are not opposed. Some often say that Compliance guarantees the efficacy and that Procedure guarantees fundamental rights, the protection of the one must result in the diminution of the guarantee of the other. It is false. As this decision shows it, through the key notion of sensitive personal data protection (heart of Compliance Law) and the care for procedure (equivalence between communication and inspection procedures; contradictory organization of the examination of sensitive personal data), we see once again that two branches of Law express the same care, have the same objective: protecting people.  The judge is able to immediately find an operational solution, proposing "an alternative procedure" axed around the principle of contradictory and conciliating Commision's and Facebook's interests has shown that it was able to bring alternative solutions to the one it suspends the execution, appropriate solution to the situation and which equilibrate the interest of both parties.  The best Ex Ante is the one which anticipate the Ex Post by the pre-constitution of evidence. Thus the firm must be able to prove later the concern that it had for human rights, here of employees, to not being exposed to sanctioning pubic authorities. This Ex Ante probatory culture is required not only from firms but also from public authorities which also have to give justification of their action.    -    
Articles

FRISON-ROCHE, Marie-Anne

💬 “Health Data Hub est un coup de maître du Conseil d’État” (“Health Data Hub is a stroke of genius of the Conseil d’État”)

Full reference: Frison-Roche, M.-A., "Health Data Hub est un coup de maître du Conseil d'État", interview realized by Olivia Dufour for Actu-juridiques, Lextenso, 22nd of October 2020 Read the news of 19th of October 2020 of the Newsletter MAFR – Law, Compliance, Regulation on which relies this interview: Conditions for the legality of a platform managed by an American company hosting European health data​: French Conseil d'État decision  To go further, on the question of Compliance Law concerning Health Data Protection, read the news of 25th of August 2020: The always in expansion "Right to be Forgotten"​: a legitimate Oxymore in Compliance Law built on Information. Example of​ Cancer Survivors Protection 

Articles

Conditions for the legality of a platform managed by an American company hosting European health data​: French Conseil d’État decision

Full reference: Frison-Roche, M.-A., Conditions for the legality of a platform managed by an American company hosting European health data​: French Conseil d'État decision, Newsletter MAFR – Law, Compliance, Regulation, 19th of October 2020 Read by freely subscribing the other news of the Newsletter MAFR – Law, Compliance, Regulation -   News Summary: In its ordinance of 13th of October 2020, Conseil national du logiciel libre (called Health Data Hub), the Conseil d'État (French Administrative Supreme Court) has determined the legal rules governing the possibility to give the management of sensitive data on a platform to a non-europeans firm, through the specific case of the decree and of the contract by which the management of the platform centralizing health data to fight against Covid-19 has been given to the Irish subsidiary of an American firm, Microsoft.  The Conseil d'État used firstly CJEU case law, especially the decision of 16th of July 2020, called Schrems 2, in the light of which it was interpreted and French Law and the contract linking GIP and The Conseil d'État concluded that it was not possible to transfer this data to United-Sates, that the contract could be only interpreted like this and that decree and contract's modifications secured this. But it observed that the risk of obtention by American public authorities was remaining.  Because public order requires the maintenance of this platform and that it does not exist for the moment other technical solution, the Conseil d'État maintained the principle of its management by Microsoft, until a European operator is found. During this, the control by the CNIL (French Data Regulator), whose the observations has been taken into consideration, will be operated.  We can retain three lessons from this great decision: There is a perfect continuum between Ex Ante and Ex Post, because by a referred, the Conseil d'État succeed in obtaining an update of the decree, a modification of the contractual clauses by Microsoft and of the words of the Minister in order to, as soon as possible, the platform is managed by an European operator. Thus, because it is Compliance Law, the relevant time of the judge is the future.  The Conseil d'État put the protection of people at the heart of its reasoning, what is compliant to the definition of Compliance Law. It succeeded to solve the dilemma: either protecting people thanks to the person to fight against the virus, or protecting people by preventing the centralization of data and their captation by American public authorities. Through a "political" decision, that is an action for the future, the Conseil found a provisional solution to protect people against the disease and against the dispossession of their data, requiring that an European solution is found.  The Conseil d'État emphasized the Court of Justice of The European Union as the alpha and omega of Compliance Law. By interpreting the contract between a GIP (Public interest Group) and an Irish subsidy of an American group only with regards to the case law of the Court of Justice of European Union, the Conseil d'Etat shows that sovereign Europe of Data can be built. And that courts are at the heart of this.  -   Read the interview given on this Ordinance Health Data Hub   To go further about the question of Compliance Law concerning health data protection, read the news of 25th of August 2020: The always in expansion "Right to be Forgotten"​: a legitimate Oxymore in Compliance Law built on Information. Example of​ Cancer Survivors Protection   

Jurisprudence

Court of Justice of the European Union

Judgment C-623/17 of 6th of October 2020 concerning the processing of personal data in the electronic communications sector

Full reference: CJEU, Grand Chamber, 6th of October 2020, Privacy International c/ Secretary of State for Foreign and Commonwealth Affairs, C-623/17. Read the judgment  Read the summary of the judgment (in French) Read the opinion of the Advocate General  Read the reference for a preliminary ruling from the Investigatory Powers Tribunal – London (United Kingdom)

Reports

Commission Nationale de l'Informatique et des Libertés (CNIL)

Lignes directrices et recommendations de la CNIL sur les cookies et autres traceurs (CNIL’s guidelines and recommendation about cookies and other trackers)

Full reference of the guidelines: Commission Nationale de l'Informatique et des Libertés (CNIL), Délibération n°2020-091 du 17 septembre 2020 portant adoption de lignes directrices relatives à l'application de l'article 82 de la loi du 6 janvier 1978 modifiée aux opérations de lecture et écriture dans le terminal d'un utilisateur (notamment aux "cookies et autres traceurs") et abrogeant la délibération n°2019-093 du 4 juillet 2019  Full reference of the recommendation: Commission Nationale de l'Informatique et des Libertés (CNIL), Délibération n°2020-092 du 17 septembre 2020 portant adoption d'une recommandation proposant des modalités pratiques de mise en conformité en cas de recours aux "cookies et autres traceurs".  Read the guidelines (in French) Read the recommendation (in French) Read the presentation of these guilines and of this recommendation by the CNIL (in French)  Read Marie-Anne Frison-Roche's comment about this in the Newsletter MAFR – Law, Regulation & Compliance of 1st of October 2020

Articles

Responding to an email with “serious anomalies”​,transferring personal data, blocks reimbursement by the bank: French Cour de cassation, July 1st 2020

Full reference: Frison-Roche, M.-A., Responding to an email with "serious anomalies"​,transferring personal data, blocks reimbursement by the bank: French Cour de cassation, July 1st 2020, Newsletter MAFR – Law, Compliance, Regulation, 10th of September 2020 Read by freely subscribing other news of the Newsletter MAFR – Law, Compliance, Regulation   Summary of the news "Phishing" is a kind of cyber criminality aiming to obtain, by sending fraudulent emails which look like to those sent by legitimate organisms, recipient's personal information in order to impersonate or steal him or her. As it is difficult to find the authors of "phishing" and to prove their intentionality in order to punish them directly, on mean to fight against "phishing" could be to entitle banks to secure their information network and, to accompany this obligation with a strong incentive, to convict them to reimburse the victims in case of robbery of their personal data.   In 2015, a client victime of this kind of fraud asked to his bank, the Crédit Mutuel, to reimburse him the amount stole, what the bank refused to do on the grounds that the client committed a fault, transferring its confidential information without checking the email, however grossly counterfeit. The Court of first instance gave reason to the client because although he committed this fault, he was in good faith. This judgment was broken by the Chambre commerciale de la Cour de cassation (French Judicial Supreme Court) by a decision of 1st of July 2020 which states that this serious negligence, exclusive of any consideration of good faith, justifies the absence of reimbursement by the bank. -   From this particular case, we can draw three lessons:  The Cour de Cassation states that good faith is not a salient criterion and that, as the bank must react when a banking account is objectively abnormal, the client must react face to an obviously abnormal email.  The Cour de Cassation describes the repartition of proof burden. Proof obligations are alternatively distributed between the bank and its client. First, the bank must secure its information network but, secondly, the client must take every reasonable measure to preserve its safety. It results from this that, if the email seems normal, phishing damages must be supported by the bank, and more generally of by the firm, while if the email is obviously abnormal, they must be supported by the client, but the burden to prove the abnormality of the email must be supported by the firm and not by the client.  Such a proof system shows that Compliance Law includes a pedagogic mission by educating each client in order to he or she would be able to distinguish among his or her emails, those which are normal and those which are obviously suspect. This pedagogic dimension, with the legal consequences associated to it, will not stop to spread.    -

Articles

For regulating or supervising, technical competence is required: example of the French creation of the “Pôle d’expertise de la régulation numérique “​

Full reference: Frison-Roche, M.-A., For regulating or supervising, technical competence is required: example of the French creation of the "Pôle d'expertise de la régulation numérique"​, Newsletter MAFR – Law, Regulation, Compliance, 2nd of September 2020 Lire par abonnement gratuit d'autres news de la Newsletter MAFR – Law, Regulation, Compliance   Summary of the news Through a decree of 31st of August 2020, the government created a national service, the "Pôle d'expertise de la régulation numérique" (digital regulation expertise pole). It has to furnish to State services a technical expertise in computer science, data science and algorithm processes in order to assist them in their role of control, investigation and study. The aim is to favor information sharing between researchers and State services in charge of regulating digital space.  As its acronym indicates, this pole of expertise aims to represents constance in a changing world. Moreover, more than being a national service, this organism must adopt a transversal dimension, its creation decree being signed by the Prime Minister, Minister of Economy, Minister of Culture and Minister of Digital Transition. The creation of such a pole shows the awareness of the government of the importance of technical competency in the regulation of digital space and of the necessity to centralize these expertises in one organ.  However, as the decree indicates, this pole of expertise could be consulted only by "State services", that excludes regulators which are independent from the State and which could put the pole in conflict of interest, and courts even if they are supposed to play a central role in the regulation of digital space and even if they are allowed to ask the advice of the regulator about some cases. But if regulators cannot size the pole, to whom does it benefit except the legislator and a few officials?  It would therefore have been better for this pole of expertise to be placed under the direction of regulatory and supervisory bodies, which would have enabled it to be able to be consulted both by regulators and by judges, both of whom are key players in digital regulation.